

[Jun-2026] Valid Way To Pass Fortinet Exam Dumps with FCP_GCS_AD-7.6 Exam Study Guide
All FCP_GCS_AD-7.6 Dumps and FCP - Google Cloud Security 7.6 Administrator Training Courses Help candidates to study and pass the Exams hassle-free!
Fortinet FCP_GCS_AD-7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
| Topic 5 |
|
| Topic 6 |
|
| Topic 7 |
|
| Topic 8 |
|
| Topic 9 |
|
| Topic 10 |
|
| Topic 11 |
|
| Topic 12 |
|
| Topic 13 |
|
| Topic 14 |
|
| Topic 15 |
|
| Topic 16 |
|
NEW QUESTION # 12
Your organization is running an application in their shared services virtual public cloud (VPC) and must control network access natively in the cloud.
How can your organization meet this requirement?
- A. Create a firewall policy for the entire VPC that allows access from all networks.
- B. Create another VPC in front of the shared services VPC and deploy FortiGate.
- C. Create a firewall rule that allows access to the application instance only.
- D. Create IAM access to allow access from specified resources only.
Answer: C
Explanation:
Creating specific firewall rules that restrict access directly to the application instance allows precise native network access control within the shared services VPC.
NEW QUESTION # 13
Your organization is deciding between deploying FortiGate active-passive high-availability (HA) in Google Cloud using either the software-defined network (SDN) connector or load balancers.
What two reasons should your organization choose the SDN connector over the load balancer deployment?
(Choose two.)
- A. Failovers are faster because of to API calls.
- B. Cost is lower.
- C. There isess administrative overhead.
- D. The SDN connector supports multizone failover.
Answer: B,C
Explanation:
Using the SDN connector avoids additional load balancer costs, making it more cost-effective.
The SDN connector enables multizone failover by directly managing network routing, which load balancers do not inherently support.
NEW QUESTION # 14
What are the two responsibilities of a Google Cloud customer in terms of security? (Choose two.)
- A. The Google Cloud customer is responsible for securing network traffic.
- B. The Google Cloud customer is responsible for securing operating systems and applications.
- C. The Google Cloud customer is responsible for securing the computing resources.
- D. The Google Cloud customer is responsible for securing cloud storage infrastructure.
Answer: A,B
Explanation:
Customers manage security for their data, applications, operating systems, and network configurations, while Google secures the underlying cloud infrastructure.
NEW QUESTION # 15
An administrator is tasked to deploy two FortiGate devices in two different zoned to achieve geographical redundancy.
Which two architectural considerations must the administrator address? (Choose two.)
- A. The FortiGate devices must be deployed in two different regions.
- B. The FortiGate devices can be deployed in the same subnet.
- C. The FortiGate devices cannot be assigned the second IP address in the subnets that they are deployed in.
- D. The FortiGate devices must not be deployed in the same VPC.
Answer: A,C
Explanation:
Deploying FortiGate devices in different regions ensures geographic redundancy.
The second IP address in a subnet is reserved for the default gateway in Google Cloud, so FortiGate devices cannot use that IP.
NEW QUESTION # 16
Google Cloud network services offer vast functionality and inter-connectivity between the cloud and on- premises networks.
Which three additional functions does FortiGate offer when deployed in Google Cloud to complement the native services offered by Google Cloud? (Choose three.)
- A. Secure SD-WAN with application visibility
- B. SSL VPN
- C. SSL inspection
- D. OSPF over IPSec
- E. Web filtering
Answer: A,B,C
Explanation:
FortiGate provides SSL VPN capabilities for secure remote access.
It offers SSL inspection to decrypt and inspect encrypted traffic for threats.
FortiGate supports Secure SD-WAN with deep application visibility and control, enhancing network performance and security beyond native Google Cloud services.
NEW QUESTION # 17
Your organization has decided to deploy a high-availability (HA) cluster. One kye requirement of the deployment is to support configuration synchronization.
Which three deployment types should be considered? (Choose three.)
- A. Active-active HA using auto scaling
- B. Active-passive HA using FGSP
- C. Active-passive HA using software-defined networking (SDN)
- D. Active-passive HA using passthrough load balancers
Answer: B,C,D
Explanation:
These three deployment types support configuration synchronization between HA cluster members, which is critical for maintaining consistent state and seamless failover.
NEW QUESTION # 18
For what three reasons must you deploy a set of Google Cloud passthrough network load balancers for an active-passive high-availability (HA) FortiGate cluster instead of a set of Google Cloud proxy network load balancers? (Choose three.)
- A. Passthrough network load balancers rely on API calls from FortiGate devices during HA failovers.
- B. Passthrough network load balancers terminate SSL connections.
- C. Passthrough network load balancers offer the highest throughput.
- D. Passthrough network load balancers can forward all protocols.
- E. Passthrough network load balancers support health checks.
Answer: C,D,E
Explanation:
Passthrough load balancers support health checks to monitor backend health for failover.
They can forward all protocols, not limited to HTTP/HTTPS like proxy load balancers.
Passthrough load balancers provide higher throughput because they don't terminate sessions.
NEW QUESTION # 19
Refer to the exhibit.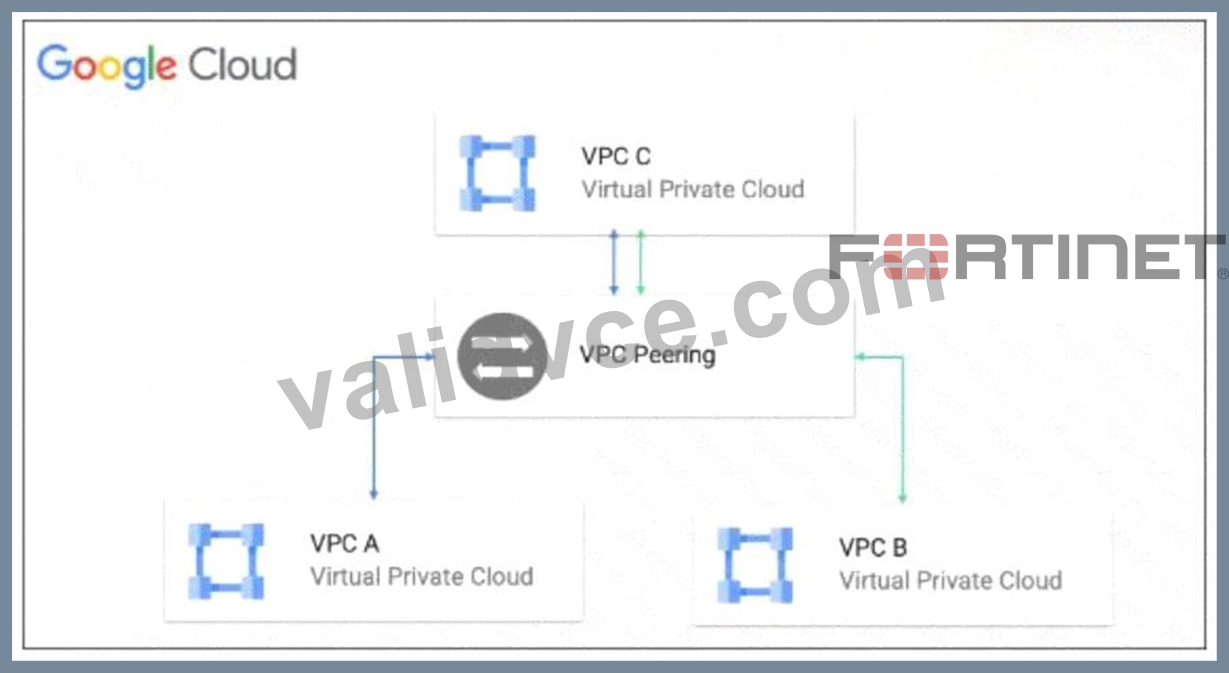
Which action must the administrator take to route traffic from VPC B to VPC A?
- A. The administrative must configure a custom route in VPC B and point the gateway to VPC A.
- B. The administrator must deploy a FortiGate VM with at least three network interfaces.
- C. The administrator must configure a custom route in VPC B and point the gateway to the VPC peering service.
- D. The administrator must create a new VPC peering connection between VPC A and VPC B.
Answer: B
Explanation:
Because VPC peering is non-transitive, traffic cannot route from VPC B to VPC A via VPC C. To enable routing between VPC A and VPC B through VPC C, a FortiGate VM with multiple network interfaces can act as a firewall/router to manage traffic between the three VPCs.
NEW QUESTION # 20
An organization has decided to deploy an active-active high-availability cluster in Google Cloud.
Which three load balancing features are critical to the successful deployment of the cluster? (Choose three.)
- A. The health check used by the internal and the external passthrough network load balancer
- B. The forwarding rule for the internal passthrough network load balancer as the next hot for custom routes
- C. The symmetric hashing of the internal passthrough network load balancer
- D. The session termination of the external passthrough network load balancer
- E. The L3_DEFAULT protocol in the forwarding rule of the internal passthrough network load balancer
Answer: A,B,C
Explanation:
Health checks ensure load balancers route traffic only to healthy cluster members.
Forwarding rules act as next hops in routing, directing traffic appropriately within the HA cluster.
Symmetric hashing ensures consistent and balanced traffic distribution across cluster members, critical for active-active deployments.
NEW QUESTION # 21
You have been tasked with destroying all resources relating to a recent active-active high-availability (HA) FGSP Terraform deployment in Google Cloud.
What steps do you have to take to ensure a successful deletion? (Choose two.)
- A. Delete all dependencies to resources relating to the Terraform template.
- B. Delete all resources manually because active-active HA clusters cannot be destroyed using Terraform.
- C. Use the command terraform destroy to delete all resources deployed by the Terraform template.
- D. Use the command terraform plan before destroying the Terraform template.
Answer: A,C
Explanation:
Removing dependencies prevents resource conflicts during deletion.
terraform destroy is the correct command to cleanly and completely remove all resources created by the Terraform deployment.
NEW QUESTION # 22
An organization is planning to deploy two FortiGate VMs in two different regions.
Which two Google Cloud core components can span both FortiGate VMs in both regions? (Choose two.)
- A. Google Cloud zone
- B. Google Cloud virtual private cloud
- C. Google Cloud subnet
- D. Google Cloud project
Answer: B,D
Explanation:
A Google Cloud VPC can span multiple regions, allowing FortiGate VMs in different regions to be part of the same network.
A Google Cloud project provides the administrative boundary that can include resources across multiple regions and VPCs, enabling centralized management of both FortiGate VMs.
NEW QUESTION # 23
A cloud administrator is tasked with protecting web applications hosted in Google Cloud.
Which three cloud offerings can the administrator use to accomplish the task? (Choose three.)
- A. FortiWeb Cloud
- B. FortiWeb VM
- C. Google Cloud IAM
- D. Google Cloud Armor
- E. Google Cloud Run
Answer: A,B,D
Explanation:
FortiWeb VM is a web application firewall (WAF) deployed on Google Cloud to protect web apps.
Google Cloud Armor provides DDoS and application-level protection.
FortiWeb Cloud offers cloud-native WAF services to protect applications hosted in Google Cloud.
NEW QUESTION # 24
Your organization has deployed an active-active high-availability (HA) FortiGate cluster in Google Cloud.
You have noticed a significant increase in asymmetrical traffic flow.
Which two actions can you take to mitigate the issue? (Choose two.)
- A. Enable destination NAT for ingress traffic.
- B. Enable the layer 3 unified threat management (UTM) scanning feature if the FortiGate devices are on ForiOS 6.4 or later.
- C. Enable symmetric hashing on the external load balancer.
- D. Enable source NAT for ingress traffic.
Answer: C,D
Explanation:
Enabling source NAT ensures consistent source IPs, promoting symmetric traffic flow.
Symmetric hashing on the load balancer helps distribute traffic flows evenly and consistently across cluster members, reducing asymmetric routing.
NEW QUESTION # 25
A cloud administrator has been receiving reports of slow response times from users accessing their organization's web application, which is protected by FortiWeb Cloud.
Which two steps can be taken to potentially alleviate the problem? (Choose two.)
- A. Changing the DNS records to point to the web application.
- B. Enabling the content delivery network (CDN).
- C. Adding additional passthrough load balancers.
- D. Deploying FortiWeb Cloud in the same region where the web application is hosted.
Answer: B,D
Explanation:
Deploying FortiWeb Cloud closer to the web application reduces latency and improves response times.
Enabling CDN caches content closer to users, reducing load times and speeding up content delivery.
NEW QUESTION # 26
You have been tasked with deploying an active-active FortiGate high-availability cluster in Google Cloud.
How can you ensure that traffic will flow symmetrically?
- A. Deploy internal passthrough network load balancers on both sides of the cluster they support symmetric hashing.
- B. There is no need to ensure traffic symmetry because FortiGate can effectively inspect asymmetric traffic.
- C. Google Cloud performs NAT on incoming traffic for external passthrough network load balancers. No action is needed.
- D. Enable the layer 3 unified threat management scanning feature on FortiGate.
Answer: A
NEW QUESTION # 27
......
Real Exam Questions and Answers - Fortinet FCP_GCS_AD-7.6 Dump is Ready: https://drive.google.com/open?id=15gVq_0S7Wiq9POhR4hCtH2_1T97Dd1Tv
Get Latest [Jun-2026] Conduct effective penetration tests using ValidVCE FCP_GCS_AD-7.6: https://www.validvce.com/FCP_GCS_AD-7.6-exam-collection.html
