

Best Fortinet FCP_FSM_AN-7.2 Exam Practice Material Updated on Sep 28, 2026
New FCP_FSM_AN-7.2 Actual Exam Dumps, Fortinet Practice Test
Fortinet FCP_FSM_AN-7.2 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
NEW QUESTION # 24
Refer to the exhibit.
Which two conditions will match this rule and subpatterns? (Choose two.)
- A. A user fails twice to log in when connecting through RDP.
- B. A user using RDP over SSL VPN fails to log in to an application five times.
- C. A user connects to the wrong IP address for an RDP session five times.
- D. A user runs a brute force password cracker against an RDP server.
Answer: B,D
Explanation:
The user initiates an RDP session (Subpattern 1) and then fails to log in multiple times (Subpattern 2 with COUNT(Matched Events) >= 3) - both from the same Source IP and User within 300 seconds.
The brute force attempts typically involve a successful RDP connection followed by multiple failed logins, satisfying the sequence and grouping conditions in the rule.
NEW QUESTION # 25
Which information can FortiSIEM retrieve from FortiClient EMS through an API connection?
- A. Host login credentials
- B. Host software versions
- C. ZTNA tags
- D. FortiSIEM license
Answer: C
Explanation:
FortiSIEM can retrieve ZTNA tags from FortiClient EMS through an API connection, enabling dynamic user and device classification for policy enforcement and incident response.
NEW QUESTION # 26
Which analytics search can be used to apply a user and entity behavior analytics (UEBA) tag to an event for a failed login by the user JSmith?
- A. Username NOT END WITH jsmith
- B. User = smith
- C. Username CONTAIN smit
- D. User IS jsmith
Answer: D
Explanation:
The correct syntax to match an exact username in FortiSIEM analytics search is User IS jsmith.
This ensures that the UEBA tag is applied only when the event is specifically tied to the user
"jsmith", which is required for accurate behavioral analytics.
NEW QUESTION # 27
Refer to the exhibit.
Which two conditions will match this rule and subpatterns? (Choose two.)
- A. A user fails twice to log in when connecting through RDP.
- B. A user using RDP over SSL VPN fails to log in to an application five times.
- C. A user connects to the wrong IP address for an RDP session five times.
- D. A user runs a brute force password cracker against an RDP server.
Answer: B,D
Explanation:
The user initiates an RDP session (Subpattern 1) and then fails to log in multiple times (Subpattern 2 with COUNT(Matched Events) >= 3) - both from the same Source IP and User within 300 seconds.
The brute force attempts typically involve a successful RDP connection followed by multiple failed logins, satisfying the sequence and grouping conditions in the rule.
NEW QUESTION # 28
Refer to the exhibit.
An analyst is trying to identify an issue using an expression based on the Expression Builder settings shown in the exhibit; however, the error message shown in the exhibit indicates that the expression is invalid.
What is the correct syntax to create an expression that generates a total count of matched events?
- A. (COUNT) Matched Events
- B. COUNT(Matched Events)
- C. Matched Events (COUNT)
- D. Matched Events COUNT()
Answer: B
Explanation:
The correct syntax is COUNT(Matched Events) - with proper capitalization and spacing - to generate a total count of matched events. The error in the exhibit likely stems from a formatting issue (e.g., lowercase count() or incorrect spacing), not the logical structure of the expression.
NEW QUESTION # 29
Refer to the exhibit.
What is the Group: FortiSIEM Analysts value referring to?
- A. LDAP user group
- B. Windows Active Directory user group
- C. CMDB user group
- D. FortiSIEM organization group
Answer: C
Explanation:
In FortiSIEM, the value Group: FortiSIEM Analysts under the User attribute refers to a CMDB user group. These groups are defined within FortiSIEM's CMDB and used to logically organize users for analytics, correlation rules, and reporting.
NEW QUESTION # 30
Refer to the exhibit.
Which two lookup types can you reference as the subquery in a nested analytics query? (Choose two.)
- A. SNMP Query
- B. CMDB Query
- C. LDAP Query
- D. Event Query
Answer: A,D
Explanation:
In FortiSIEM nested analytics queries, you can reference both CMDB Queries and Event Queries as subqueries. These allow correlation between CMDB data and event data for advanced detection use cases.
NEW QUESTION # 31
Refer to the exhibit. What will FortiSIEM display if you apply the Group By and Display Fields configuration to a list of allowed firewall connections?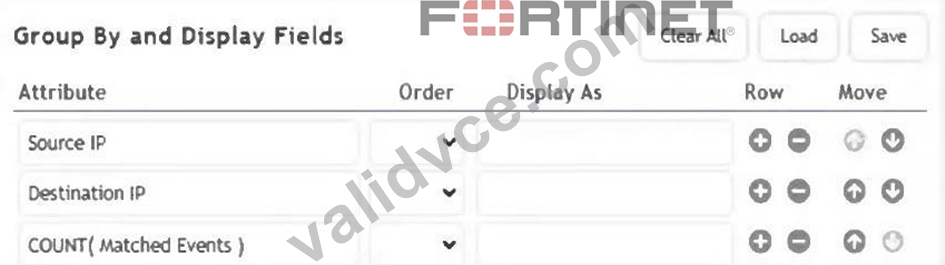
- A. A list of connections ordered by destination IP address hit count
- B. A list of connections ordered by the number of unique connections started by each source IP address
- C. A list of connections between unique source and destination IP addresses
- D. A running count of connections, regardless of source or destination
Answer: C
Explanation:
With Source IP and Destination IP as grouping attributes, and COUNT(Matched Events) included, FortiSIEM will display a list of unique source-destination IP pairs along with the number of allowed connections between each pair. This configuration summarizes connection activity by unique communication paths.
NEW QUESTION # 32
You need a model for predicting a target field based on other fields in a dataset and then trigger an anomaly if the value does not match the prediction. Which machine learning algorithm will build this type of model?
- A. Clustering
- B. Regression
- C. Regression
- D. Forecasting
Answer: B
Explanation:
A Regression algorithm is used when predicting a continuous or numeric target field based on other features in the dataset. In FortiSIEM, regression-based machine learning models establish expected values, and an anomaly is triggered when the actual observed value significantly deviates from the regression prediction.
NEW QUESTION # 33
What must you configure to apply ZTNA tags from FortiSIEM to devices in FortiClient EMS?
- A. API connection from FortiSIEM to FortiClient EMS
- B. Syslog connection to FortiSIEM from FortiGate firewalls
- C. Syslog connection to FortiGate firewalls from FortiSIEM
- D. API connection from FortiClient EMS to FortiSIEM
Answer: A
NEW QUESTION # 34
Refer to the exhibit.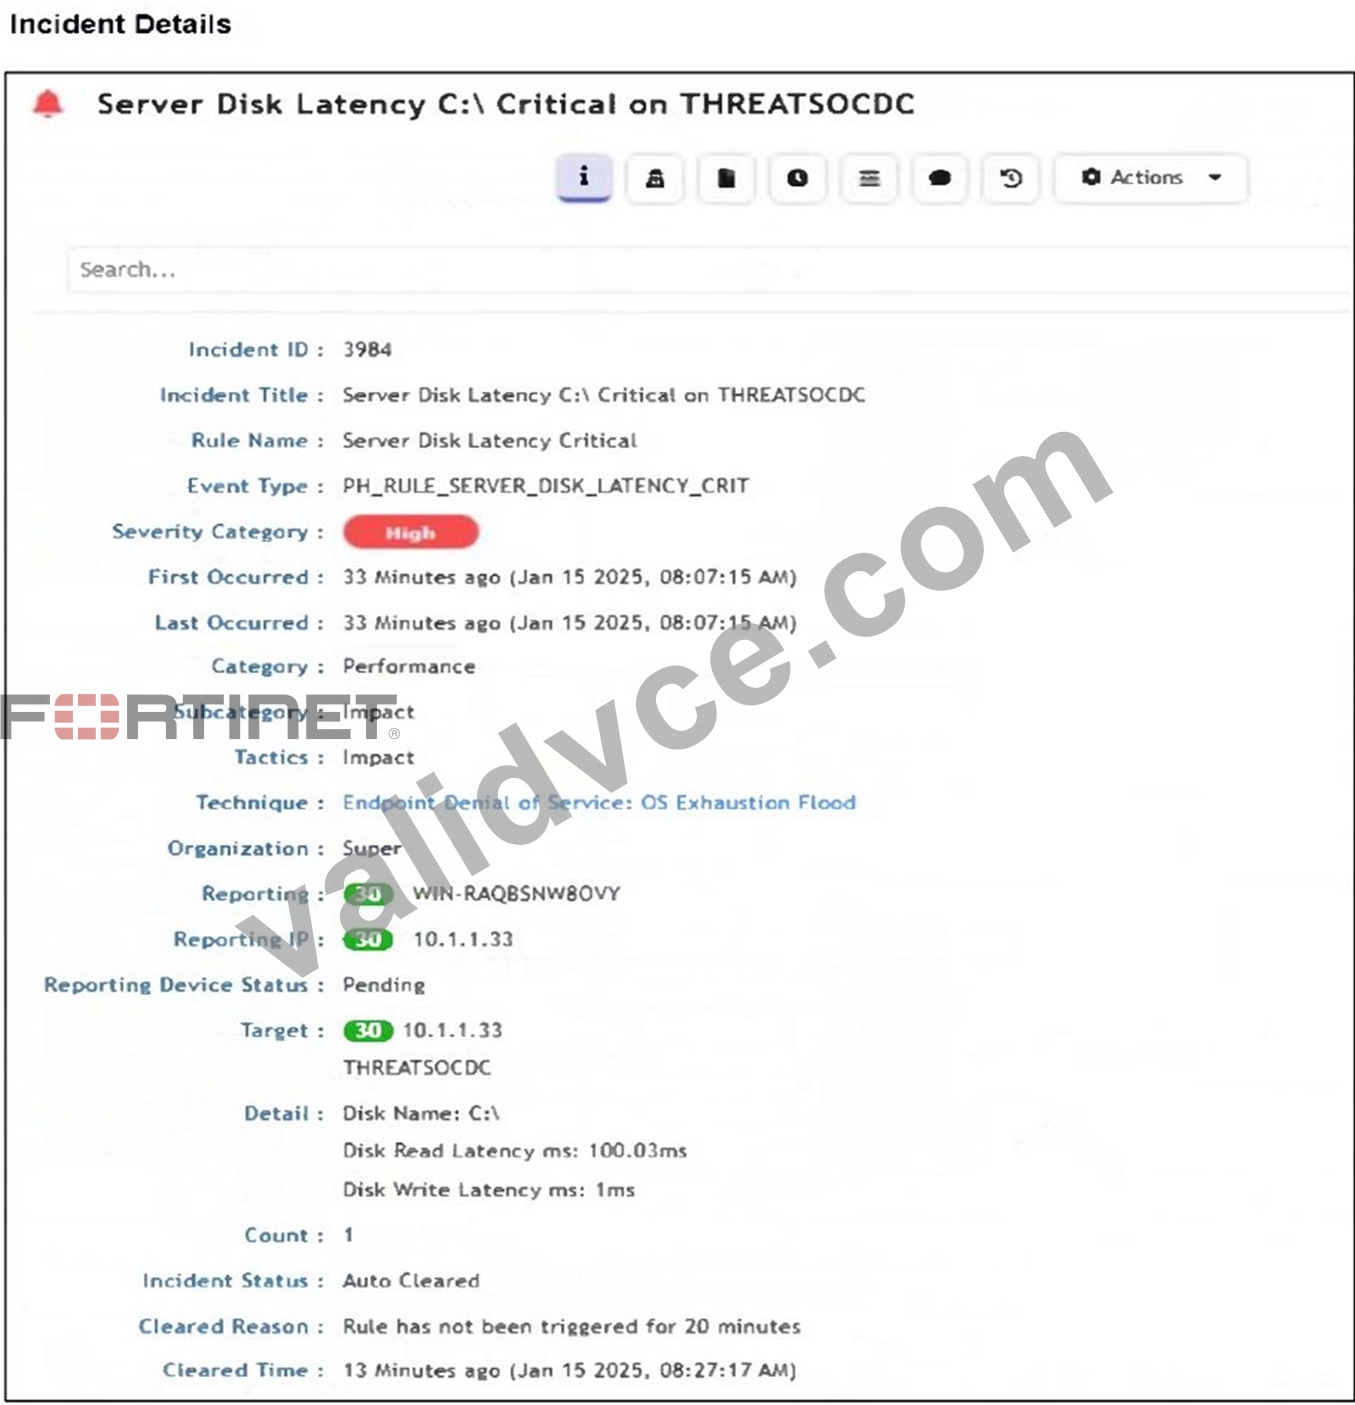
How was this incident cleared?
- A. The incident was cleared automatically by the rule.
- B. The endpoint was rebooted and sent an all-clear signal to FortiSIEM.
- C. The analyst manually cleared the incident from the incident table.
- D. FortiSIEM cleared the incident automatically after 24 hours.
Answer: A
Explanation:
The Incident Status shows "Auto Cleared", and the Cleared Reason states: "Rule has not been triggered for 20 minutes." This indicates that the incident was automatically cleared by the rule logic after a defined period of inactivity.
NEW QUESTION # 35
What must match when referencing an inner query from an outer query?
- A. Both must reference IP addresses.
- B. Both must be event queries.
- C. Both must be CMDB lookups.
- D. Both must have the same data type.
Answer: D
Explanation:
When creating an inner query in FortiSIEM, the referenced attribute in the outer and inner queries must share the same data type (for example, IP address, string, or integer). This ensures the system can properly correlate and filter results between the two queries during execution.
NEW QUESTION # 36
Refer to the exhibit.
A FortiSIEM analyst is investigating an issue by examining events related to two destination IP addresses. However, the analyst is not getting any results from the search.
Based on the selected filters shown in the exhibit, why is the search returning no results?
- A. The wrong option is selected in the Operator column.
- B. Parentheses are missing between the two items.
- C. The wrong boolean operator is selected in the Next column.
- D. An invalid IP address is typed in the Value column.
Answer: C
Explanation:
The boolean operator between the two destination IP filters is set to AND, meaning FortiSIEM searches for events where the Destination IP is simultaneously 10.10.10.1 and 192.168.1.1, which is impossible. Changing the operator to OR would return events matching either IP address, producing the expected results.
NEW QUESTION # 37
Refer to the exhibit.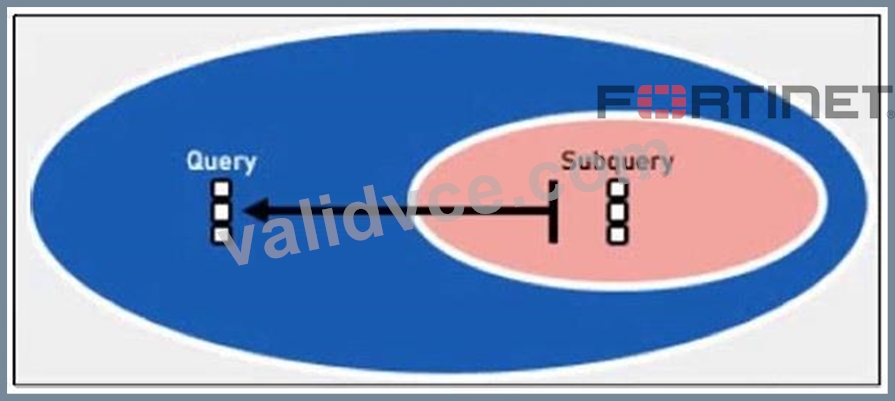
Which two lookup types can you reference as the subquery in a nested analytics query? (Choose two.)
- A. SNMP Query
- B. LDAP Query
- C. Event Query
- D. CMDB Query
Answer: C,D
Explanation:
In FortiSIEM nested analytics queries, you can reference both CMDB Queries and Event Queries as subqueries. These allow correlation between CMDB data and event data for advanced detection use cases.
NEW QUESTION # 38
When configuring anomaly detection machine learning, in which step must you select the fields to analyze?
- A. Schedule
- B. Train
- C. Prepare Data
- D. Design
Answer: C
Explanation:
In the Prepare Data step of configuring anomaly detection in FortiSIEM, you must select the fields to analyze. This step defines the input features that the machine learning model will evaluate during training and detection.
NEW QUESTION # 39
Refer to the exhibit.
An analyst is trying to generate an incident with a title that includes the Source IP, Destination IP, User, and Destination Host Name. They are unable to add a Destination Host Name as an incident attribute.
What must be changed to allow the analyst to select Destination Host Name as an attribute?
- A. The Destination Host Name must be selected as a Triggered Attribute.
- B. The Destination IP Event Attribute must be removed.
- C. The Destination Host Name must be set as an aggregate item in a subpattern.
- D. The Destination Host Name must be added as an Event type in the FortiSIEM.
Answer: A
Explanation:
For an attribute like Destination Host Name to be used in the incident title, it must first be included in the Triggered Attributes list. Only attributes listed there are available for substitution in the title template (e.g., $destIpAddr, $srcIpAddr).
NEW QUESTION # 40
Refer to the exhibit.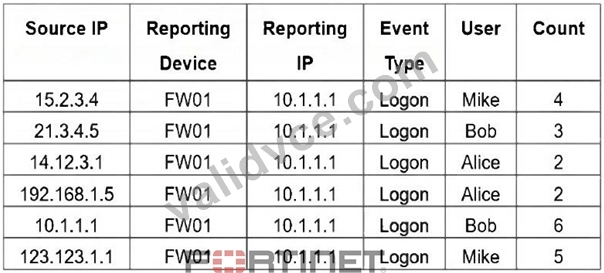
If you group the events by User, Source IP, and Count attributes, how many results will FortiSIEM display?
- A. Six
- B. Five
- C. Three
- D. Two
- E. Four
Answer: A
Explanation:
Grouping by User, Source IP, and Count means that each unique combination of those three attributes will be treated as a separate result. In the table, all six rows have distinct combinations of User, Source IP, and Count - so FortiSIEM will display 6 results.
NEW QUESTION # 41
Refer to the exhibit.
A FortiSIEM device is receiving syslog events from a FortiGate firewall. The FortiSIEM analyst is trying to search the raw event logs for the last two hours that contain the keyword "udp". However, they are getting no results from the search, which they know should be available. Based on the filter shown in the exhibit, why are there no search results?
- A. The analyst selected = in the Operator column. That is the wrong operator.
- B. The Time Range value should be set to Real-Time.
- C. The keyword is case sensitive. Instead of typing udp in the Value field, the analyst should type UDP.
- D. The analyst selected AND in the Next column. This is the wrong Boolean operator.
Answer: A
Explanation:
The operator is set to "=", which performs an exact match on the entire raw event log, not a substring search. To find logs that contain the keyword "udp", the analyst should use the CONTAIN operator instead. This will return all logs where "udp" appears anywhere in the raw log message.
NEW QUESTION # 42
Refer to the exhibit.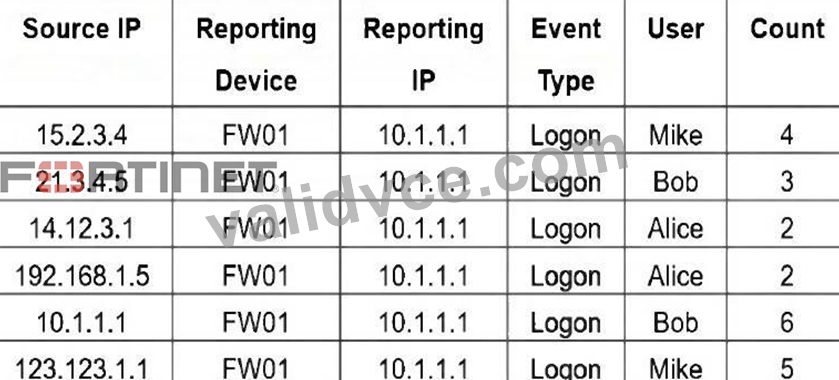
If you group the events by User, Source IP, and Count attributes, how many results will FortiSIEM display?
- A. Six
- B. Five
- C. Three
- D. Two
- E. Four
Answer: A
Explanation:
Grouping by User, Source IP, and Count means that each unique combination of those three attributes will be treated as a separate result. In the table, all six rows have distinct combinations of User, Source IP, and Count - so FortiSIEM will display 6 results.
NEW QUESTION # 43
Which statement about thresholds is true?
- A. FortiSIEM uses fixed, hardcoded global and device thresholds for all performance metrics.
- B. FortiSIEM uses only global thresholds for performance metrics.
- C. FortiSIEM uses only device thresholds for security metrics.
- D. FortiSIEM uses global and per device thresholds for performance metrics.
Answer: D
Explanation:
FortiSIEM evaluates performance metrics against both global thresholds, which apply system-wide, and per-device thresholds, which can be customized for individual devices. This dual approach allows flexibility in monitoring while ensuring consistent baseline alerting.
NEW QUESTION # 44
Which two settings must you configure to allow FortiSIEM to apply tags to devices in FortiClient EMS? (Choose two.)
- A. ZTNA tags defined on FortiSIEM
- B. Remediation script configured
- C. FortiSIEM API credentials defined on FortiEMS\
- D. FortiEMS API credentials defined on FortiSIEM
Answer: C,D
Explanation:
To allow FortiSIEM to apply tags to devices in FortiClient EMS, FortiEMS API credentials must be defined on FortiSIEM to enable communication with EMS, and FortiSIEM API credentials must be defined on FortiEMS to allow EMS to accept tagging instructions from FortiSIEM. This bidirectional API trust is essential for tag application.
NEW QUESTION # 45
Refer to the exhibit.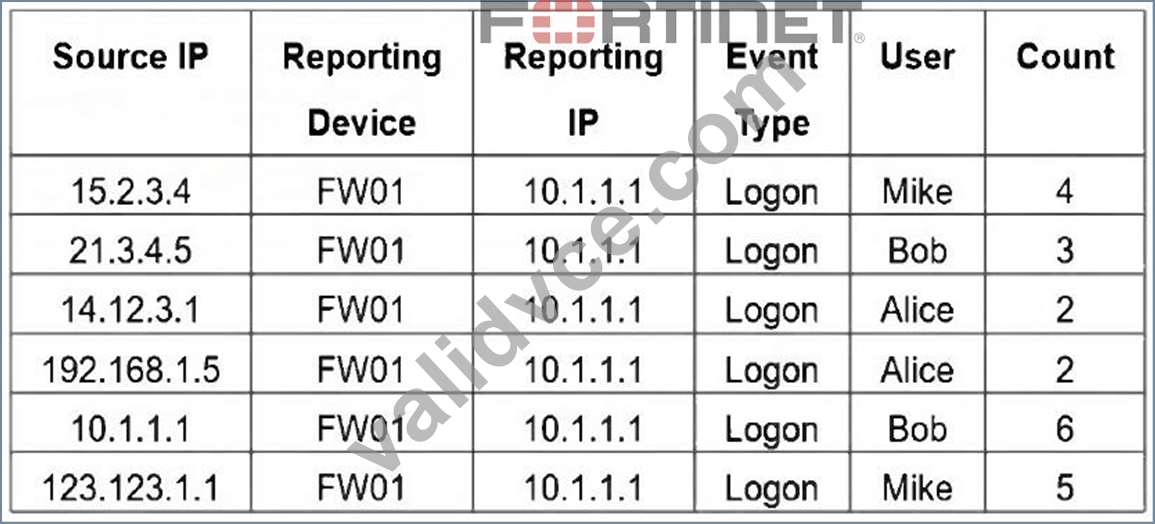
If you group the events by User and Count attributes, how many results will FortiSIEM display?
- A. Six
- B. Five
- C. One
- D. Three
- E. Two
Answer: B
Explanation:
Grouping by User and Count yields five unique pairs: (Mike,4), (Bob,3), (Alice,2), (Bob,6), (Mike,5).
NEW QUESTION # 46
Which two elements can you use to define how an automation policy activates? (Choose two.)
- A. Watchlist
- B. Lookup table
- C. Rules
- D. Time range
Answer: C,D
NEW QUESTION # 47
......
Study HIGH Quality FCP_FSM_AN-7.2 Free Study Guides and Exams Tutorials: https://www.validvce.com/FCP_FSM_AN-7.2-exam-collection.html
Download Fortinet FCP_FSM_AN-7.2 Exam Dumps to Pass Exam Easily: https://drive.google.com/open?id=1YcKbU8zmRMAV09cguKWDxrCE778dwJkn
