

CS0-003 PDF Download Oct-2023 CompTIA Test To Gain Brilliante Result!
Provide Updated CompTIA CS0-003 Dumps as Practice Test and PDF
CompTIA Cybersecurity Analyst (CySA+) Certification, also known as the CS0-003 exam, is a globally recognized certification that validates the knowledge and skills of an individual in the field of cybersecurity analysis. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is designed for professionals who wish to specialize in the field of cybersecurity and want to enhance their skills in detecting, preventing, and responding to cybersecurity threats.
The CySA+ certification exam covers various topics such as network security, vulnerability management, threat management, incident response, and compliance and regulations. CS0-003 exam focuses on practical, hands-on skills that are required to perform the job of a cybersecurity analyst. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is ideal for individuals who are working in roles such as cybersecurity analyst, security engineer, security consultant, and network security analyst. By obtaining the CySA+ certification, professionals can demonstrate their expertise in the field of cybersecurity analysis and can enhance their career prospects.
CompTIA Cybersecurity Analyst (CySA+) Certification is recognized by employers worldwide and is in high demand. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification demonstrates that the candidate has the skills and knowledge to protect against cybersecurity threats and incidents. CompTIA Cybersecurity Analyst (CySA+) Certification Exam certification is ideal for professionals who are looking to advance their careers in cybersecurity and want to demonstrate their expertise in this field.
NEW QUESTION # 19
A security analyst is writing a shell script to identify IP addresses from the same country. Which of the following functions would help the analyst achieve the objective?
- A. function x() { info=$(geoiplookup $1) && echo "$1 | $info" }
- B. function z() { info=$(traceroute -m 40 $1 | awk 'END{print $1}') && echo "$1 | $info" }
- C. function y() { info=$(dig -x $1 | grep PTR | tail -n 1 ) && echo "$1 | $info" }
- D. function w() { info=$(ping -c 1 $1 | awk -F "/" 'END{print $1}') && echo "$1 | $info" }
Answer: A
Explanation:
The function that would help the analyst identify IP addresses from the same country is:
function x() { info=$(geoiplookup $1) && echo "$1 | $info" }
This function takes an IP address as an argument and uses the geoiplookup command to get the geographic location information associated with the IP address, such as the country name, country code, region, city, or latitude and longitude. The function then prints the IP address and the geographic location information, which can help identify any IP addresses that belong to the same country.
NEW QUESTION # 20
An analyst has been asked to validate the potential risk of a new ransomware campaign that the Chief Financial Officer read about in the newspaper. The company is a manufacturer of a very small spring used in the newest fighter jet and is a critical piece of the supply chain for this aircraft. Which of the following would be the best threat intelligence source to learn about this new campaign?
- A. Blogs/forums
- B. Information sharing organization
- C. Deep/dark web
- D. Cybersecuritv incident response team
Answer: B
Explanation:
An information sharing organization is a group or network of organizations that share threat intelligence, best practices, or lessons learned related to cybersecurity issues or incidents. An information sharing organization can help security analysts learn about new ransomware campaigns or other emerging threats, as well as get recommendations or guidance on how to prevent, detect, or respond to them. An information sharing organization can also help security analysts collaborate or coordinate with other organizations in the same industry or region that may face similar threats or challenges.
NEW QUESTION # 21
Which of the following would help to minimize human engagement and aid in process improvement in security operations?
- A. QVVASP
- B. SOAR
- C. OSSTMM
- D. SIEM
Answer: B
Explanation:
Explanation
SOAR stands for security orchestration, automation, and response, which is a term that describes a set of tools, technologies, or platforms that can help streamline, standardize, and automate security operations and incident response processes and tasks. SOAR can help minimize human engagement and aid in process improvement in security operations by reducing manual work, human errors, response time, or complexity. SOAR can also help enhance collaboration, coordination, efficiency, or effectiveness of security operations and incident response teams.
NEW QUESTION # 22
A cybersecurity analyst is researching operational data to develop a script that will detect the presence of a threat on corporate assets. Which of the following contains the most useful information to produce this script?
- A. OpenloC files
- B. Protocol analysis captures
- C. MITRE ATT&CK reports
- D. API documentation
Answer: C
Explanation:
A cybersecurity analyst is researching operational data to develop a script that will detect the presence of a threat on corporate assets. The most useful information to produce this script is MITRE ATT&CK reports. MITRE ATT&CK is a knowledge base of adversary tactics and techniques based on real-world observations. MITRE ATT&CK reports provide detailed information on how different threat actors operate, what tools they use, what indicators they leave behind, and how to detect or mitigate their attacks. The other options are not as useful or relevant for this purpose. Reference: CompTIA Cybersecurity Analyst (CySA+) Certification Exam Objectives (CS0-002), page 9; https://attack.mitre.org/
NEW QUESTION # 23
A security program was able to achieve a 30% improvement in MTTR by integrating security controls into a SIEM. The analyst no longer had to jump between tools. Which of the following best describes what the security program did?
- A. Data enrichment
- B. Single pane of glass
- C. Security control plane
- D. Threat feed combination
Answer: B
Explanation:
A single pane of glass is a term that describes a unified view or interface that integrates multiple tools or data sources into one dashboard or console. A single pane of glass can help improve security operations by providing visibility, correlation, analysis, and alerting capabilities across various security controls and systems. A single pane of glass can also help reduce complexity, improve efficiency, and enhance decision making for security analysts. In this case, a security program was able to achieve a 30% improvement in MTTR by integrating security controls into a SIEM, which provides a single pane of glass for security operations. Official Reference: https://www.eccouncil.org/cybersecurity-exchange/threat-intelligence/cyber-kill-chain-seven-steps-cyberattack
NEW QUESTION # 24
Which of the following ICS network protocols has no inherent security functions on TCP port 502?
- A. SSH
- B. DHCP
- C. CIP
- D. Modbus
Answer: D
Explanation:
Modbus is an industrial control system (ICS) network protocol that is used for communication between devices such as sensors, controllers, actuators, and monitors. Modbus has no inherent security functions on TCP port 502, which is the default port for Modbus TCP/IP communication. Modbus does not provide any encryption, authentication, or integrity protection for the data transmitted over the network, making it vulnerable to various attacks such as replay, modification, spoofing, or denial-of-service.
NEW QUESTION # 25
The vulnerability analyst reviews threat intelligence regarding emerging vulnerabilities affecting workstations that are used within the company: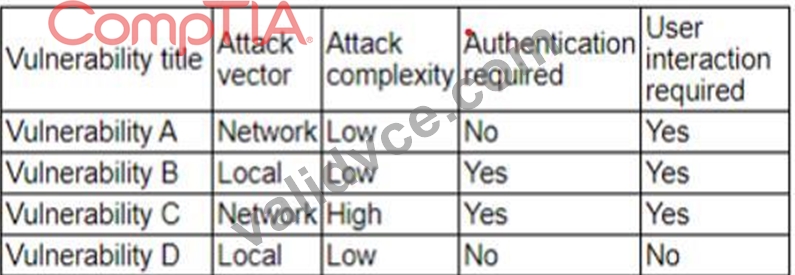
Which of the following vulnerabilities should the analyst be most concerned about, knowing that end users frequently click on malicious links sent via email?
- A. Vulnerability C
- B. Vulnerability D
- C. Vulnerability A
- D. Vulnerability B
Answer: D
Explanation:
Explanation
Vulnerability B is the vulnerability that the analyst should be most concerned about, knowing that end users frequently click on malicious links sent via email. Vulnerability B is a remote code execution vulnerability in Microsoft Outlook that allows an attacker to run arbitrary code on the target system by sending a specially crafted email message. This vulnerability is very dangerous, as it does not require any user interaction or attachment opening to trigger the exploit. The attacker only needs to send an email to the victim's Outlook account, and the code will execute automatically when Outlook connects to the Exchange server. This vulnerability has a high severity rating of 9.8 out of 10, and it affects all supported versions of Outlook.
Therefore, the analyst should prioritize patching this vulnerability as soon as possible to prevent potential compromise of the workstations.
NEW QUESTION # 26
Due to reports of unauthorized activity that was occurring on the internal network, an analyst is performing a network discovery. The analyst runs an Nmap scan against a corporate network to evaluate which devices were operating in the environment. Given the following output: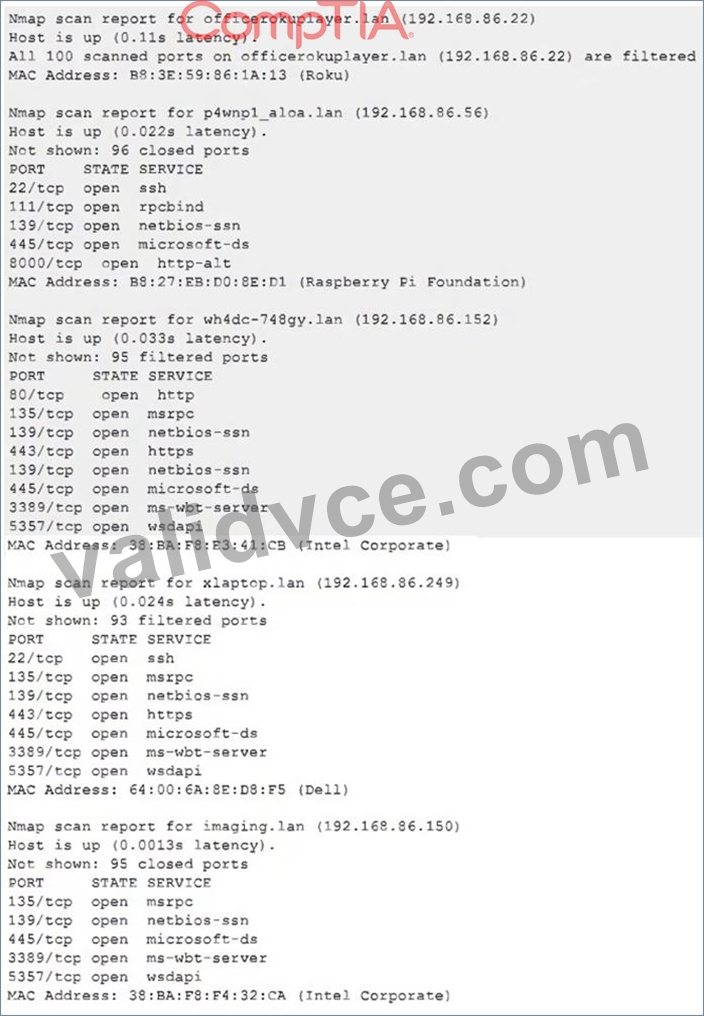
Which of the following choices should the analyst look at first?
- A. wh4dc-748gy.lan (192.168.86.152)
- B. p4wnp1_aloa.lan (192.168.86.56)
- C. imaging.lan (192.168.86.150)
- D. lan (192.168.86.22)
- E. xlaptop.lan (192.168.86.249)
Answer: B
Explanation:
Explanation
The analyst should look at p4wnp1_aloa.lan (192.168.86.56) first, as this is the most suspicious device on the network. P4wnP1 ALOA is a tool that can be used to create a malicious USB device that can perform various attacks, such as keystroke injection, network sniffing, man-in-the-middle, or backdoor creation. The presence of a device with this name on the network could indicate that an attacker has plugged in a malicious USB device to a system and gained access to the network. Official References:
https://github.com/mame82/P4wnP1_aloa
NEW QUESTION # 27
An older CVE with a vulnerability score of 7.1 was elevated to a score of 9.8 due to a widely available exploit being used to deliver ransomware. Which of the following factors would an analyst most likely communicate as the reason for this escalation?
- A. Weaponization
- B. CVSS
- C. Scope
- D. Asset value
Answer: A
Explanation:
Weaponization is a factor that describes how an adversary develops or acquires an exploit or payload that can take advantage of a vulnerability and deliver a malicious effect. Weaponization can increase the severity or impact of a vulnerability, as it makes it easier or more likely for an attacker to exploit it successfully and cause damage or harm. Weaponization can also indicate the level of sophistication or motivation of an attacker, as well as the availability or popularity of an exploit or payload in the cyber threat landscape. In this case, an older CVE with a vulnerability score of 7.1 was elevated to a score of 9.8 due to a widely available exploit being used to deliver ransomware. This indicates that weaponization was the reason for this escalation.
NEW QUESTION # 28
As a proactive threat-hunting technique, hunters must develop situational cases based on likely attack scenarios derived from the available threat intelligence information. After forming the basis of the scenario, which of the following may the threat hunter construct to establish a framework for threat assessment?
- A. Threat vector
- B. Critical asset list
- C. Hypothesis
- D. Attack profile
Answer: C
Explanation:
A hypothesis is a statement that can be tested by threat hunters to establish a framework for threat assessment. A hypothesis is based on situational awareness and threat intelligence information, and describes a possible attack scenario that may affect the organization. A hypothesis can help to guide threat hunters in their investigation by providing a clear and specific question to answer, such as "Is there any evidence of lateral movement within our network?" or "Are there any signs of data exfiltration from our servers?".
NEW QUESTION # 29
Which of the following would a security analyst most likely use to compare TTPs between different known adversaries of an organization?
- A. OWASP
- B. STIXTAXII
- C. Cyber Kill Cham
- D. MITRE ATTACK
Answer: D
Explanation:
Explanation
MITRE ATT&CK is a framework and knowledge base that describes the tactics, techniques, and procedures (TTPs) used by various adversaries in cyberattacks. MITRE ATT&CK can help security analysts compare TTPs between different known adversaries of an organization, as well as identify patterns, gaps, or trends in adversary behavior. MITRE ATT&CK can also help security analysts improve threat detection, analysis, and response capabilities, as well as share threat intelligence with other organizations or communities
NEW QUESTION # 30
The Chief Executive Officer of an organization recently heard that exploitation of new attacks in the industry was happening approximately 45 days after a patch was released. Which of the following would best protect this organization?
- A. A mean time to detect of 45 days
- B. A mean time to remediate of 30 days
- C. A mean time to respond of 15 days
- D. Third-party application testing
Answer: B
Explanation:
Explanation
A mean time to remediate (MTTR) is a metric that measures how long it takes to fix a vulnerability after it is discovered. A MTTR of 30 days would best protect the organization from the new attacks that are exploited 45 days after a patch is released, as it would ensure that the vulnerabilities are fixed before they are exploited
NEW QUESTION # 31
A recent penetration test discovered that several employees were enticed to assist attackers by visiting specific websites and running downloaded files when prompted by phone calls. Which of the following would best address this issue?
- A. Blocking all scripts downloaded from the internet
- B. Increasing training and awareness for all staff
- C. Disabling all staff members' ability to run downloaded applications
- D. Ensuring that malicious websites cannot be visited
Answer: B
Explanation:
Explanation
Increasing training and awareness for all staff is the best way to address the issue of employees being enticed to assist attackers by visiting specific websites and running downloaded files when prompted by phone calls.
This issue is an example of social engineering, which is a technique that exploits human psychology and behavior to manipulate people into performing actions or divulging information that benefit the attackers.
Social engineering can take many forms, such as phishing, vishing, baiting, quid pro quo, or impersonation.
The best defense against social engineering is to educate and train the staff on how to recognize and avoid common social engineering tactics, such as:
Verifying the identity and legitimacy of the caller or sender before following their instructions or clicking on any links or attachments Being wary of unsolicited or unexpected requests for information or action, especially if they involve urgency, pressure, or threats Reporting any suspicious or anomalous activity to the security team or the appropriate authority Following the organization's policies and procedures on security awareness and best practices Official References:
https://partners.comptia.org/docs/default-source/resources/comptia-cysa-cs0-002-exam-objectives
https://www.comptia.org/certifications/cybersecurity-analyst
https://www.comptia.org/blog/the-new-comptia-cybersecurity-analyst-your-questions-answered
NEW QUESTION # 32
Which of the following is the BEST option to protect a web application against CSRF attacks?
- A. Set a server-side rate limit for CSRF token generation.
- B. Avoid the transmission of CSRF tokens using cookies.
- C. Configure the web application to only use HTTPS and TLS 1.3.
- D. Update the web application to the latest version.
Answer: B
Explanation:
CSRF tokens are random values that are generated by the server and included in requests that perform state-changing actions. They are used to prevent CSRF attacks by verifying that the request originates from a legitimate source. However, if the CSRF tokens are transmitted using cookies, they are vulnerable to being stolen or forged by an attacker who can exploit other vulnerabilities, such as cross-site scripting (XSS) or cookie injection. Therefore, a better option is to avoid the transmission of CSRF tokens using cookies and use other methods, such as hidden form fields or custom HTTP headers. Reference: CompTIA Cybersecurity Analyst (CySA+) Certification Exam Objectives (CS0-002), page 11; https://owasp.org/www-community/attacks/csrf
NEW QUESTION # 33
Which of the following is the best reason why organizations need operational security controls?
- A. To supplement areas that other controls cannot address
- B. To limit physical access to areas that contain sensitive data
- C. To assess compliance automatically against a secure baseline
- D. To prevent disclosure by potential insider threats
Answer: A
Explanation:
Operational security controls are security measures that are implemented and executed by people rather than by systems. Operational security controls are needed to supplement areas that other controls, such as technical or physical controls, cannot address. For example, operational security controls can include policies, procedures, training, awareness, audits, reviews, testing, etc. These controls can help ensure that employees follow best practices, comply with regulations, detect and report incidents, and respond to emergencies. The other options are not specific to operational security controls or are too narrow in scope. Reference: CompTIA Cybersecurity Analyst (CySA+) Certification Exam Objectives (CS0-002), page 14; https://www.isaca.org/resources/isaca-journal/issues/2016/volume-3/operational-security-controls
NEW QUESTION # 34
......
CS0-003 Dumps are Available for Instant Access: https://www.validvce.com/CS0-003-exam-collection.html
Valid CS0-003 Dumps for Helping Passing CS0-003 Exam!: https://drive.google.com/open?id=1gwoedLeLS2lKR7wQVpbzLItImRu3baIO
