

Real NSE6_WCS-6.4 are Uploaded by ValidVCE provide 2023 Latest NSE6_WCS-6.4 Practice Tests Dumps.
All NSE6_WCS-6.4 Dumps and Fortinet NSE 6 - Securing AWS With Fortinet Cloud Security 6.4 Training Courses Help candidates to study and pass the Fortinet NSE 6 - Securing AWS With Fortinet Cloud Security 6.4 Exams hassle-free!
NEW QUESTION 16
Refer to the exhibit.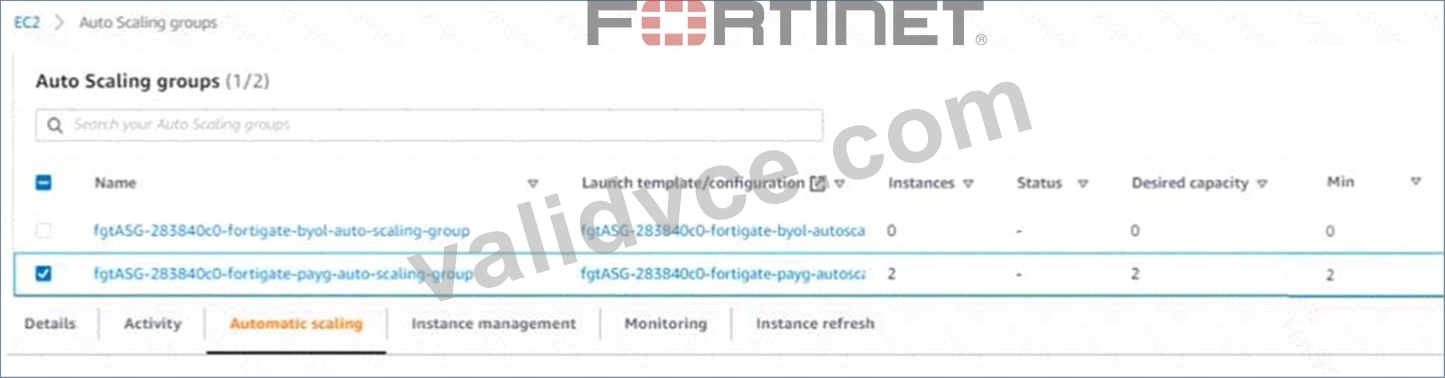
An administrator configured two auto-scaling polices that they now want to test, What Will be the impact on payg-auto-scaling-group for the FortiGate devices if the administrator executes a scale-in policy?
- A. The scale-in policy will decrease instances from two to one.
- B. The scale-in policy will decrease the number of maximum instances from four to three.
- C. The scale-in policy will decrease the desired capacity from two to one
Answer: B
NEW QUESTION 17
Which statement is true about an Elastic Network Interface (ENI)?
- A. When youmove an ENI, network traffic is not redirected to the new instance.
- B. Once ENI detaches from one instance. it cannot reattach to another instance.
- C. An ENI cannot move between AZs.
- D. You can detach primary ENI from an AWS instance.
Answer: C
NEW QUESTION 18
Refer to the exhibit.
An administrator wants to update the database package from
the Internet to a database server configured with IP address
Which statement is correct about traffic from server IP address
10.0.1.7 to the internet. based on the diagrarm?
- A. Traffic from server10.0.1.7 to the internet will hide
behind elastic IP 198.51.100.4 - B. Traffic from server 10.0.1.7 to the internet will hide
behind elastic IP 198.51.100.1 - C. Traffic from server 10.0.1.7 to the internet will hide
behind elastic IP 198.51.100.3 - D. Traffic from server 10.0.1.7 to the internet will hide
behind elastic IP 198.51.100 2.
Answer: A
NEW QUESTION 19
You want to deploy FortiGate for AWS to protect your production network in the cloud. but you do not need the 2417 support available in the enterprise bundle.
Which license model do you choose?
- A. Pay as a bundle (PAYB).
- B. Bring your own device (BYOD)
- C. pay as you go (PAYG).
- D. Bring your own license (BYOL).
Answer: C
NEW QUESTION 20
An MSSP deployed 16 FortiGate VMS With the default AWS security groups and network access lists using an on-demand license from Amazon Web Services (AWS) Marketplace. They are using a third-party configuration backup application to back up and track changes for the FortiGate configurations. It can connect to the FortiGatedevices using only the SSH protocol, A customer is using the correct username and password configured on the FortiGate devices. but they are unable to log in using theSSH protocol.
What can be the reason Why this authentication is failing?
- A. The default AWS network access list for FortiGate does not allow SSH.
- B. AWS uses non-standard SSH port1025, and the default AWS security groups and NACL for FortiGate are not configured for the port.
- C. The AWS key is required to log in to FortiGate using SSH
- D. The default AWS Security group for FortiGate does not allow SSH.
Answer: C
NEW QUESTION 21
An administrator has deployed an environment in AWS and is now trying to send outbound traffic from the web servers to the internet through FortiGate. The FortiGate policies are configured to allow all outbound traffic. however. the traffic is not reaching the FortiGate internal interface.
Which two statements Can be the reasons for this behavior? (Choose two )
- A. AWS security groups are blocking the traffic.
- B. Internet Gateway (IGW) is not configured for VPC.
- C. AWS source destination checks are enabled on the FortiGate internal interfaces.
- D. FortiGate is not configured as a default gateway tor web servers.
Answer: A,C
NEW QUESTION 22
Refer to the exhibit.
A customer is using the AWS Elastic Load Balancer.
Which two statements are correct about the Elastic LoadBalancer configuration? (Choose two.)
- A. The Amazon resource name is used to access the load balancer node and targets.
- B. The load balancer is configuredfor the internal traffic oftheVPC
- C. The DNS name is used to access devices.
- D. The load balancer is configured to load balance traffic between devices in two AZS.
Answer: C,D
NEW QUESTION 23
HOW is traffic failover handled in a FortiGate active-active cluster deployed in AWS?
- A. All FortiGate cluster members use unicast FGCP_
- B. The elastic load balancer handles traffic failover using FGCP.
- C. All FortiGate cluster members send health probes using a dedicated interface.
- D. The elastic load balancer handles bi-directional traffic failover using a health probe.
Answer: D
NEW QUESTION 24
You are network connectivity issues between two VMS deployed in AWS. One VM is a FortiGate located on subnet *LAN- that is part Of the VPC "Encryption". The Other VM is a Windows server located on the subnet
"servers" Which is also in the "Encryption" VPC. You are unable to ping the Windows server from FortiGate.
What is the reason for this?
- A. The default AWS Network Access Control List (NACL) does not allow this traffic.
- B. You have not created a VPN to allow traffic between those subnets.
- C. The firewall in the Windows VM is blocking the traffic.
- D. By default. AWS does not allow ICMP traffic between subnets.
Answer: C
NEW QUESTION 25
Which two statements are correct about AWS Network Access Control Lists (NACLS)? (Choose two.)
- A. VPC automatically comes with a modifiable default NACL, and by default it denies all inbound and outbound IPv4 traffic.
- B. NACLs are stateless: responses to allowed inbound traffic are subject to the rules for outbound traffic.
- C. An NACL has separate inbound and outbound rules, and each rule can either allow or deny traffic.
- D. By default. each custom NACL allows all inbound and outbound traffic unless you add new rules,
Answer: B,C
NEW QUESTION 26
Which three statements are correct about AWS security groups? (Choose three)
- A. When associate multiple security groups With an instance, the rules from each security group are effectively aggregated to create one set Of rules
- B. By default, security groups block all outbound traffic.
- C. a Security group rules are always permissive: you cannot create rules that deny access.
- D. By default,security groups allow all inbound traffic.
- E. Security groups are statetul
Answer: A,C,E
NEW QUESTION 27
Which AWS product integrates With FortiGate to automate security remediation for workloads running on the AWS platform?
- A. AWS GuardDuty
- B. AWS Inspector
- C. AWS Protector
- D. AWS Shield
Answer: A
NEW QUESTION 28
......
Fortinet NSE6_WCS-6.4 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Valid Way To Pass Fortinet's NSE6_WCS-6.4 Exam with : https://www.validvce.com/NSE6_WCS-6.4-exam-collection.html
Free Test Engine For Fortinet NSE 6 - Securing AWS With Fortinet Cloud Security 6.4 Certification Exams: https://drive.google.com/open?id=1POVky5xG3dHSfJ_4lzseDl9LWoiuLxv2
